Security Assessment and Consulting
Strategic reviews that uncover vulnerabilities honestly, including the ones that are uncomfortable to report, with a plan built around what's actually exposed.
We pair certified security specialists with 24/7 monitoring, so hardening your defenses strengthens your compliance posture instead of complicating it.
Most breaches don't start with a sophisticated exploit. They start with a gap nobody was watching, between tools that don't talk to each other and a team stretched too thin to notice in time. We close the seams instead of adding another disconnected tool to the pile.
We identify vulnerabilities and risk honestly, including the ones a previous vendor's report conveniently left out.
Layered protection across network, endpoint, and application security closes the specific gaps your assessment found, not a generic checklist.
A security operations center provides real threat detection around the clock, with certified analysts reviewing what automated tools flag, not an alert queue nobody reads.
We stay engaged through incident response and recovery, so an incident gets contained fast and documented for the compliance review that follows.
Protect enterprise attack surfaces with zero-trust architecture, automated threat telemetry, and SOC 2 / HIPAA compliance frameworks.
Strategic reviews that uncover vulnerabilities honestly, including the ones that are uncomfortable to report, with a plan built around what's actually exposed.
Layered protection with firewalls, intrusion detection, and traffic monitoring that stops unauthorized access before it reaches anything sensitive.
Complete device protection across computers, mobile, and IoT, closing the gap attackers look for when a single unpatched device is all they need.
Testing and safeguards that catch vulnerabilities in custom and commercial applications before an attacker finds them first.
Authentication and access controls that ensure only authorized users reach sensitive systems, audited and adjusted as roles change.

Real-time, 24/7 threat monitoring with certified analysts reviewing what gets flagged, not an automated system making the call alone.
Structured protocols that contain a threat quickly and document the response, so the compliance conversation after an incident isn't a scramble.
Connecting consulting to growth & impact, bringing together news, insights, articles, and decisions that shape the future.
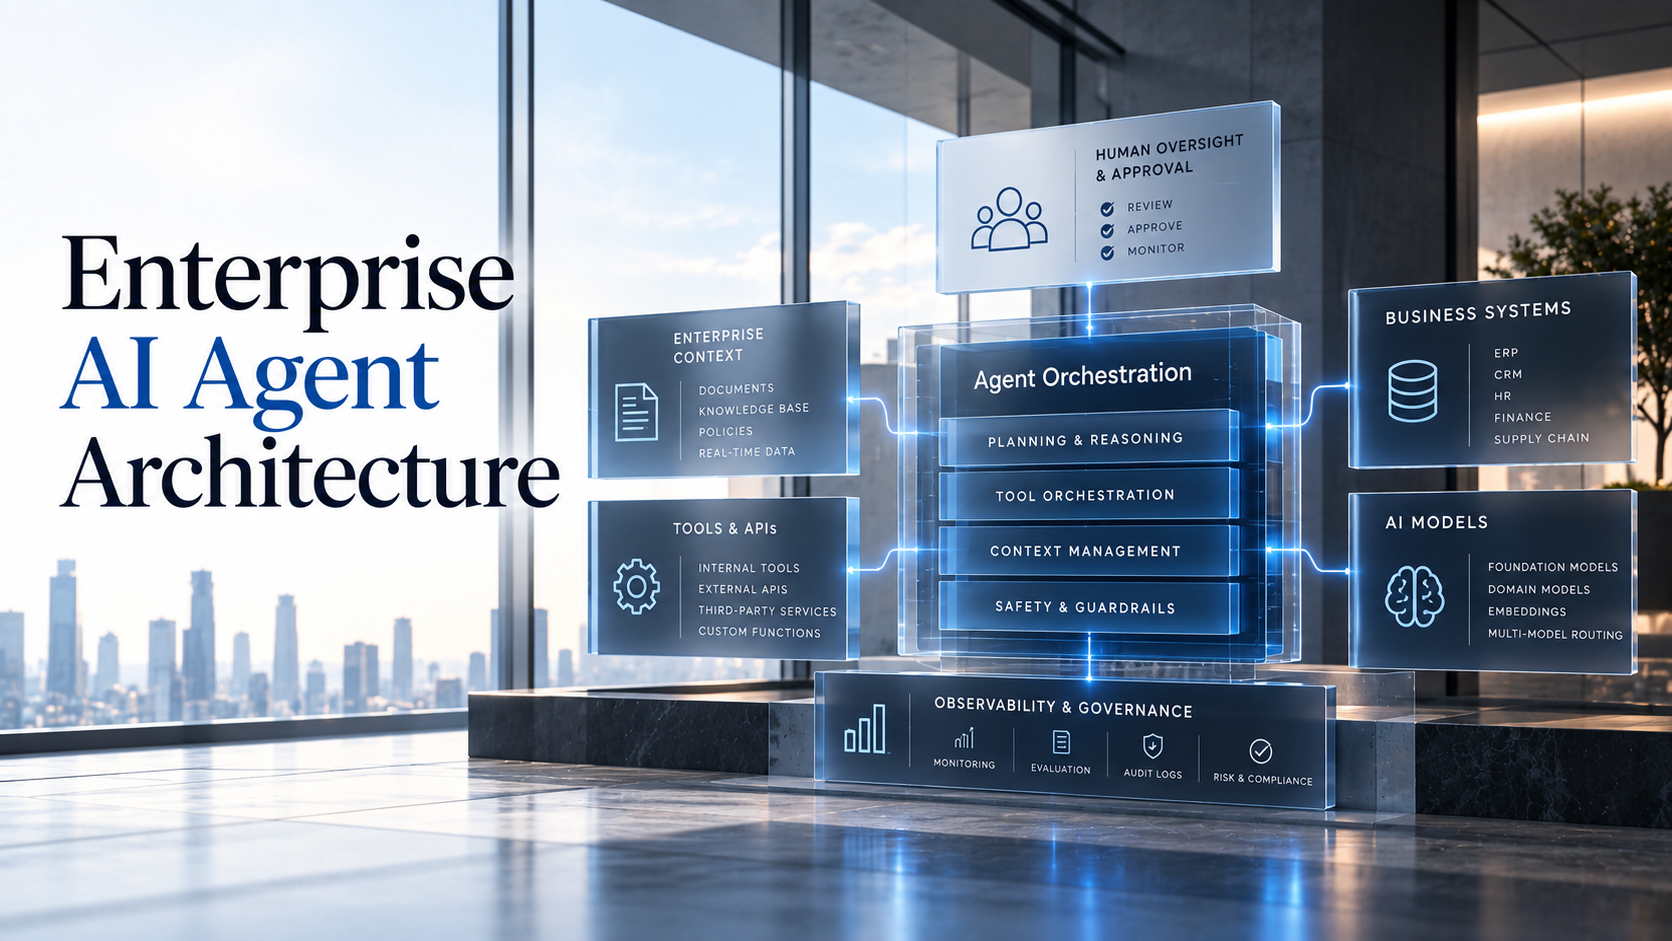
Moving AI agents from pilot to production requires more than a capable model. Explore seven architecture requirements for reliable, secure and scalable enterprise AI agents.
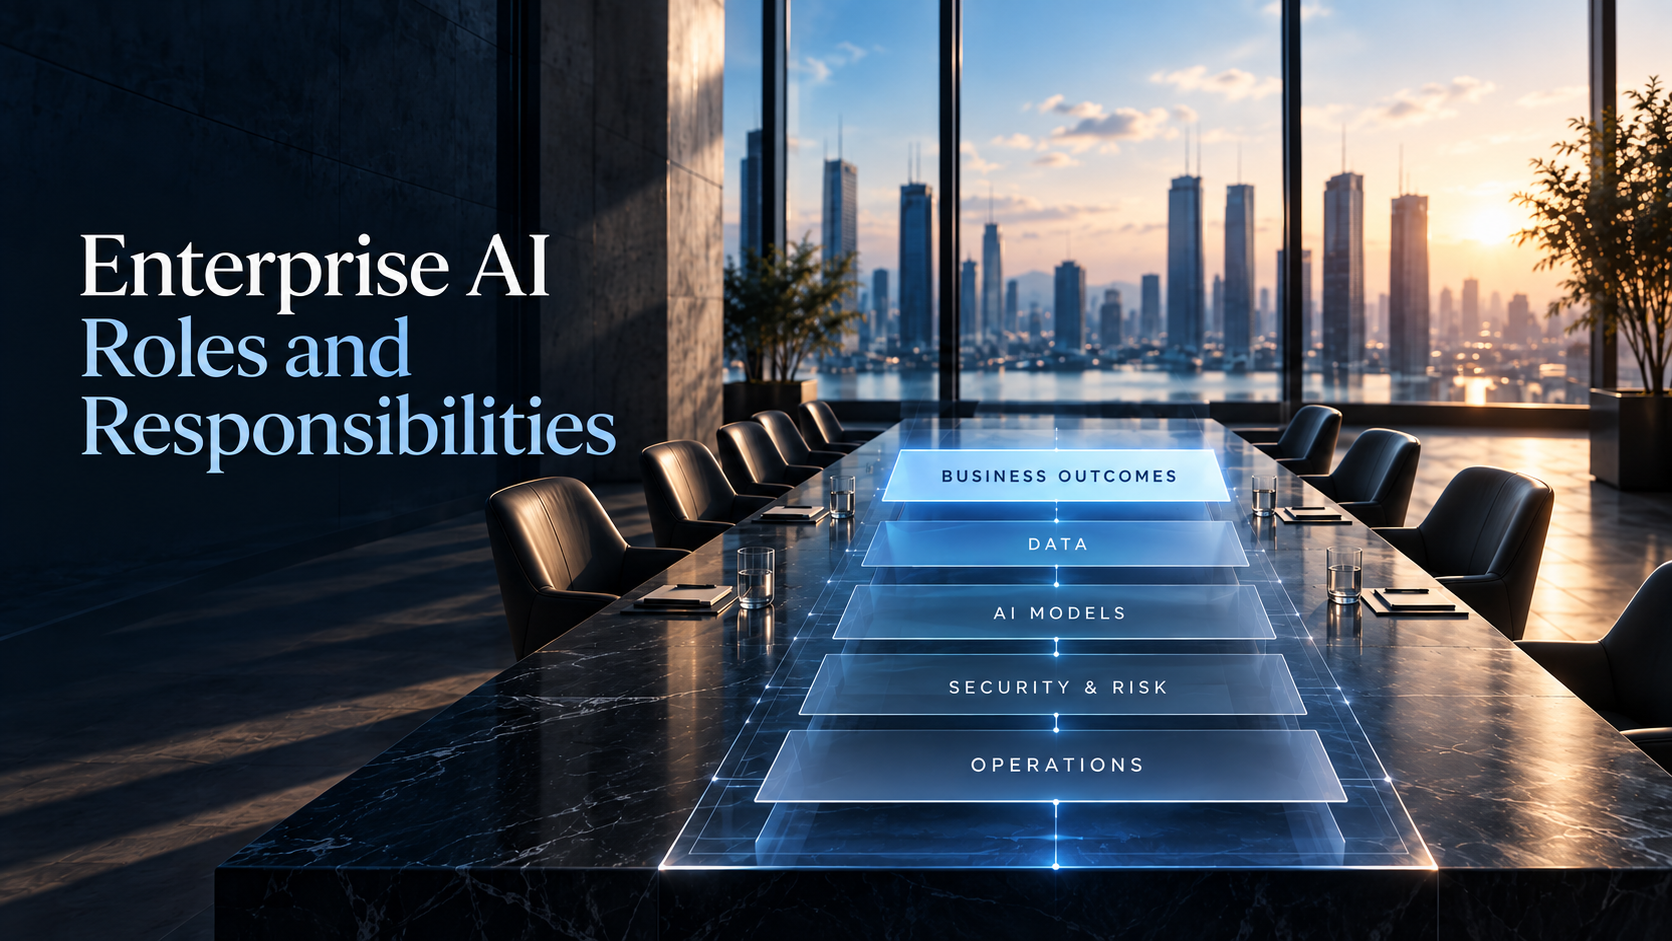
Learn how to define enterprise AI roles and responsibilities after deployment, including ownership across business, technology, data, risk, security and operations.
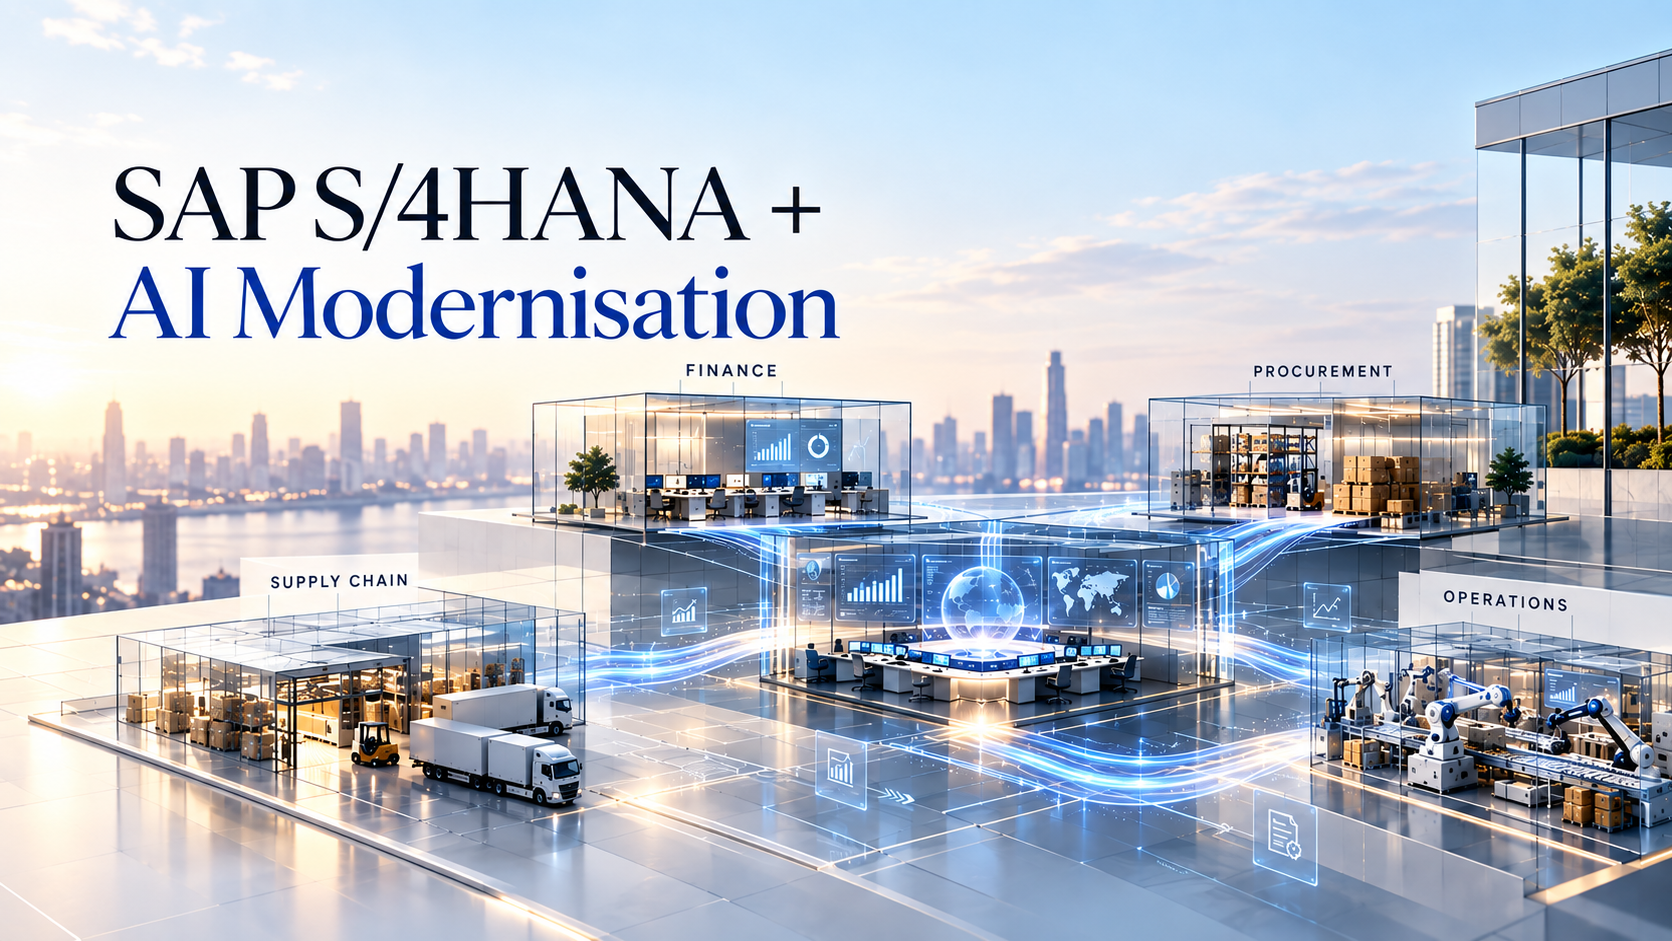
Explore where AI can add value during SAP S/4HANA modernisation, where it should wait, and how to prioritise AI without adding unnecessary complexity.
Everything you need to know about FWC's cybersecurity engineering, consulting, and deployment practices
Most breaches happen in the gap between tools that don't talk to each other, which is why our assessment stage identifies vulnerabilities honestly across your whole stack, not just the tool that's easiest to audit, and we close the seams instead of adding another disconnected point solution.
Our Security Operations Center pairs automated detection with certified analysts who review what gets flagged before anything escalates, so an alert reaching your team actually means something.
Application Security is built into the development process through testing and safeguards that catch issues early, which is faster than finding a vulnerability in production and scrambling to patch it under pressure.
Incident Response and Recovery follows structured protocols that contain a threat quickly and document every step, so the compliance conversation after an incident is a straightforward review, not a reconstruction project.
Identity and Access Management includes ongoing audit and adjustment as roles change, not a one-time setup that quietly drifts out of date as your org chart evolves.
We stay engaged through monitoring, response, and recovery as an ongoing relationship, not a one-time assessment and a report that sits in a drawer. That's the "Respond" stage in how we work, not a final deliverable.
Let’s turn business challenges into opportunities.